Repository Details
Shared by
HelloGitHub Rating
0 ratings
eBPF-based Linux Network Traffic Analysis Tool
Past 6 days Received 2 stars ✨
Use arrow keys to explore dates, Home and End for the first and last date, Escape to dismiss.| Date | Star | Daily change |
|---|---|---|
| 周日 | 2,613 | — |
| 周一 | 2,613 | 0 |
| 周二 | 2,613 | 0 |
| 周三 | 2,613 | 0 |
| 周四 | 2,615 | +2 |
| 周五 | 2,615 | 0 |
2.6k
Stars
No
Chinese
Rust
Language
Yes
Active
8
Contributors
5
Issues
No
Organization
None
Latest
76
Forks
GPL-3.0
License
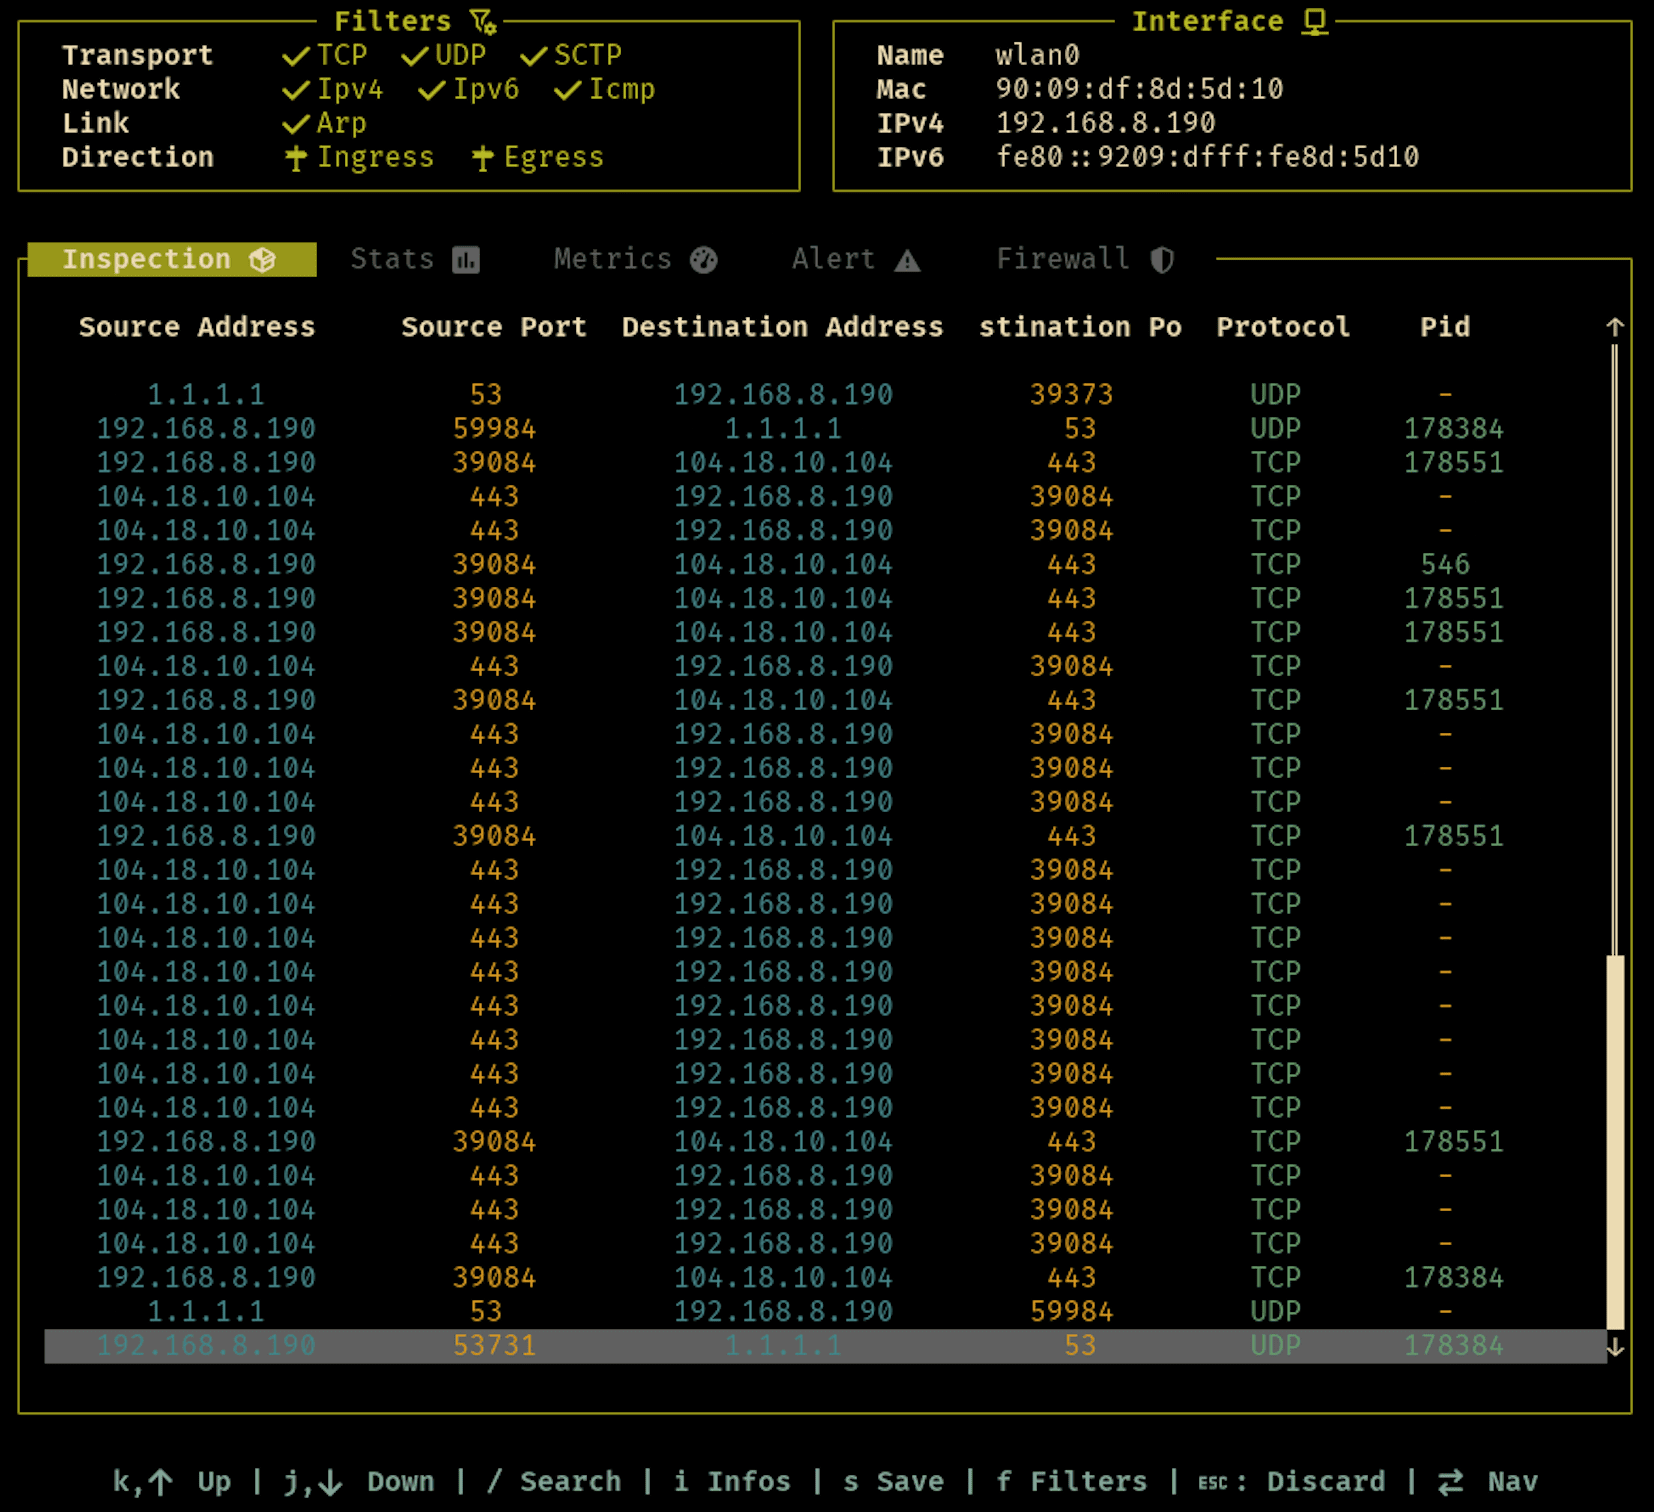
This is a network traffic sniffing and analysis tool based on eBPF technology. It can quickly open a panoramic view of network traffic on Linux. It provides a terminal visualization interface to display traffic statistics information in detail, and supports functions such as firewall rule management, fuzzy search and data export.
Comments

Rating:
No comments yet